For Enquire Call us : 9811631557
Master Offensive Security & Red Team Program
Advanced Cyber Security & Ethical Hacking – Master Offensive Security & Red Team Program
Become a Skilled Offensive Security Professional
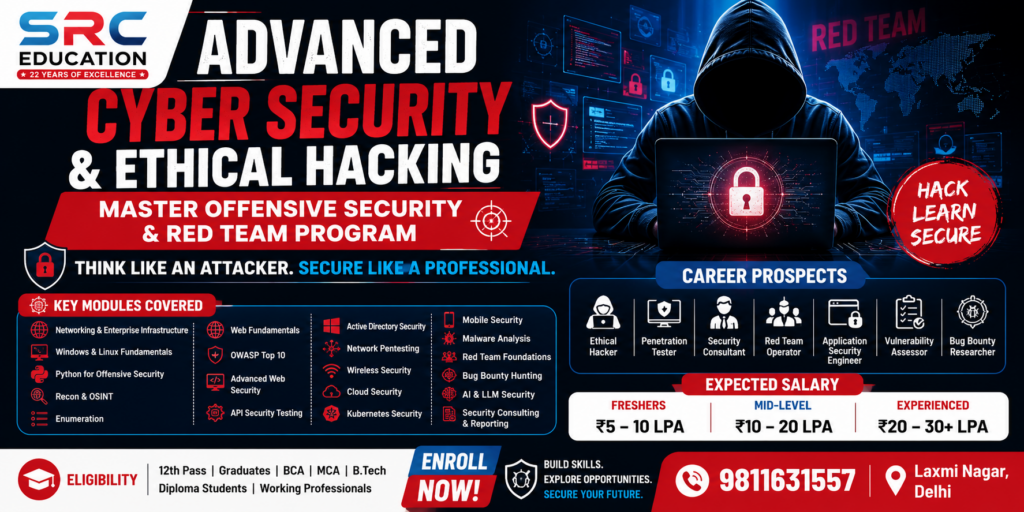
Cyber attacks are becoming more sophisticated, and organizations need security professionals who can think like attackers to identify vulnerabilities before malicious actors can exploit them. The Advanced Cyber Security & Ethical Hacking – Master Offensive Security & Red Team Program at SRC is designed for learners who want to build advanced skills in ethical hacking, penetration testing, vulnerability assessment, Red Team operations, application security, cloud security, bug bounty hunting, and offensive security.
This comprehensive program provides a structured learning path from networking and operating system fundamentals to advanced offensive security concepts. Students can learn how security professionals perform reconnaissance, enumerate systems, assess vulnerabilities, test web applications and APIs, analyze Active Directory environments, conduct network and wireless security assessments, understand cloud and Kubernetes security, and explore modern areas such as AI & LLM Security.
The program is suitable for students, graduates, IT professionals, working professionals, and aspiring cyber security specialists who want to develop practical knowledge for offensive security careers.
What is Offensive Security?
Offensive Security is a proactive approach to cyber security in which security professionals simulate real-world attacks to identify weaknesses in systems, applications, networks, cloud environments, and infrastructure.
Instead of waiting for attackers to discover vulnerabilities, ethical hackers and penetration testers legally assess an organization’s security from an attacker’s perspective.
Offensive security can involve:
- Reconnaissance and information gathering
- OSINT
- Enumeration
- Vulnerability assessment
- Web application security testing
- API security testing
- Network penetration testing
- Active Directory security assessment
- Wireless security testing
- Cloud security testing
- Mobile security testing
- Red Team operations
- Bug bounty research
- Security reporting
The objective is to identify security weaknesses responsibly and provide organizations with actionable information to strengthen their defenses.
Master Offensive Security & Red Team Program at SRC
The Master Offensive Security & Red Team Program is designed to provide learners with a broad understanding of modern offensive security.
The curriculum begins with essential networking and operating system concepts before progressing into reconnaissance, enumeration, web security, penetration testing, Active Directory, cloud security, mobile security, Red Team foundations, Bug Bounty Hunting, and AI & LLM Security.
Learners can develop an understanding of how ethical hackers and penetration testers approach security assessments and how vulnerabilities are identified, validated, documented, and responsibly reported.
Key Modules Covered
1. Networking & Enterprise Infrastructure
Networking is one of the most important foundations of cyber security and penetration testing.
This module introduces learners to enterprise networking concepts and infrastructure. Students develop an understanding of how systems communicate and how enterprise environments are structured from a security perspective.
Topics include networking fundamentals, network architecture, enterprise infrastructure, communication protocols, services, and security concepts.
A strong networking foundation helps learners understand how security vulnerabilities can affect connected systems and infrastructure.
2. Windows & Linux Fundamentals
Windows and Linux are widely used operating systems in enterprise and technology environments.
This module introduces learners to operating system fundamentals, system architecture, users, permissions, processes, services, file systems, configurations, and security concepts.
Understanding Windows and Linux environments is essential for penetration testers and offensive security professionals because security assessments frequently involve servers, workstations, applications, and infrastructure running on these platforms.
3. Python for Offensive Security
Programming knowledge can significantly improve an ethical hacker’s ability to automate repetitive security tasks and understand how security tools work.
The program introduces Python for Offensive Security, helping learners understand how programming can be applied to security-related tasks.
Students can explore concepts related to scripting, automation, data handling, security utilities, and developing customized solutions for authorized security assessments.
The goal is to help learners understand how programming and cyber security can work together.
4. Recon & OSINT
Reconnaissance is an important stage of an ethical hacking and penetration testing engagement.
During reconnaissance, security professionals collect publicly available information about the authorized target environment.
OSINT, or Open-Source Intelligence, involves gathering and analyzing information from publicly available sources.
Students learn the fundamentals of:
- Information gathering
- Target identification
- Domain and infrastructure research
- Publicly available information
- Digital footprint analysis
- OSINT methodologies
- Reconnaissance workflows
All security testing should be performed only against systems for which proper authorization has been obtained.
5. Enumeration
Enumeration involves identifying systems, services, technologies, and other relevant information within an authorized assessment scope.
This module helps learners understand how penetration testers systematically examine an environment to identify potential attack surfaces.
Students learn the concepts behind service discovery, technology identification, system enumeration, and security assessment workflows.
Web & Application Security
6. Web Fundamentals
Web applications are a major part of modern digital infrastructure.
This module provides a foundation in how websites and web applications work, including concepts related to clients, servers, requests, responses, authentication, sessions, databases, and web technologies.
Understanding these fundamentals is essential before progressing to advanced web application security testing.
7. OWASP Top 10
The OWASP Top 10 is widely referenced in application security.
Students are introduced to common categories of web application security risks and learn how security professionals assess applications for vulnerabilities.
The module focuses on understanding vulnerabilities, security risks, testing methodologies, impact assessment, and secure remediation concepts.
8. Advanced Web Security
Modern applications can contain complex architectures and security challenges.
The Advanced Web Security module takes learners beyond basic web concepts and introduces more advanced application security assessment methodologies.
Students develop an understanding of how penetration testers analyze application behavior, authentication mechanisms, access controls, input handling, sessions, and other security-sensitive components during authorized assessments.
9. API Security Testing
APIs are an essential component of modern applications, mobile applications, SaaS platforms, and cloud services.
This module introduces learners to API architecture and security testing concepts.
Students learn about common API security risks, authentication, authorization, input validation, access control, API configurations, and security assessment methodologies.
Infrastructure & Enterprise Security
10. Active Directory Security
Active Directory is widely used to manage users, computers, permissions, and resources within Windows-based enterprise environments.
This module introduces learners to Active Directory architecture and security concepts from an offensive security perspective.
Students learn how security professionals assess enterprise identity environments, identify potential weaknesses, understand privilege relationships, and evaluate security configurations during authorized penetration tests.
11. Network Pentesting
Network penetration testing involves assessing network infrastructure for security weaknesses.
This module introduces learners to network security assessment methodologies, service analysis, vulnerability identification, and penetration testing workflows.
Students develop an understanding of how security professionals evaluate network infrastructure and document security findings.
12. Wireless Security
Wireless networks introduce unique security considerations.
This module covers the fundamentals of wireless security and introduces learners to concepts related to wireless protocols, authentication, encryption, configurations, and authorized security assessments.
Students learn how wireless security weaknesses can be identified and reported responsibly.
Cloud & Modern Infrastructure Security
13. Cloud Security
Organizations increasingly rely on cloud platforms for applications, storage, computing, databases, and enterprise services.
This module introduces cloud security from an offensive security perspective.
Students learn about cloud infrastructure, identity and access management, configurations, attack surfaces, security controls, and authorized cloud security assessment concepts.
14. Kubernetes Security
Modern applications increasingly use containers and Kubernetes for deployment and infrastructure management.
This module introduces learners to Kubernetes architecture and security concepts.
Students explore areas such as container environments, Kubernetes components, configurations, access controls, workloads, and security assessment methodologies.
Understanding Kubernetes security can be valuable for professionals interested in modern cloud-native security.
15. Mobile Security
Mobile applications are an important part of today’s digital ecosystem.
This module introduces learners to mobile application security concepts and assessment methodologies.
Students learn about mobile application architecture, common security weaknesses, data protection, authentication, application behavior, and security testing concepts.
Advanced Offensive Security
16. Malware Analysis
Malware analysis helps security professionals understand how malicious software behaves.
From an offensive security learning perspective, understanding malware can provide valuable insight into attacker techniques, payload behavior, and security controls.
Students are introduced to malware concepts, analysis methodologies, indicators, behavior, and security investigation fundamentals.
The program emphasizes responsible and controlled learning environments.
17. Red Team Foundations
Red Team operations simulate realistic adversarial activity to evaluate an organization’s security posture.
This module introduces the fundamentals of Red Team operations and explains how offensive security professionals plan and conduct authorized security assessments.
Students learn about:
- Red Team methodology
- Engagement planning
- Attack simulation concepts
- Attack surface assessment
- Adversary simulation
- Security objectives
- Operational considerations
- Reporting and recommendations
The objective is to help learners understand how offensive security teams assess the effectiveness of an organization’s security controls.
18. Bug Bounty Hunting
Bug bounty programs allow security researchers to responsibly report vulnerabilities discovered within authorized programs.
This module introduces learners to Bug Bounty Hunting methodologies, vulnerability research, target analysis, web security testing, documentation, and responsible disclosure.
Students can learn how security researchers approach vulnerability discovery and communicate findings professionally.
19. AI & LLM Security
Artificial Intelligence and Large Language Models are rapidly becoming part of modern applications and business workflows.
With this growth comes a new range of security considerations.
This module introduces learners to AI & LLM Security, including security risks associated with AI-powered applications, model interactions, data handling, access control, and responsible security assessment concepts.
Understanding AI security can help learners prepare for emerging opportunities in modern cyber security.
20. Security Consulting & Reporting
Technical security skills are only one part of a professional penetration testing career. Security professionals must also be able to communicate findings clearly.
This module focuses on security reporting and consulting fundamentals.
Students learn how to document:
- Security findings
- Vulnerabilities
- Risk levels
- Potential impact
- Evidence
- Recommendations
- Remediation guidance
- Executive summaries
Professional reporting helps organizations understand security risks and prioritize remediation.
Skills You Can Develop
After completing the program, learners can develop knowledge and practical understanding in areas such as:
- Ethical Hacking
- Penetration Testing
- Offensive Security
- Red Team Operations
- Reconnaissance
- OSINT
- Enumeration
- Web Application Security
- OWASP Top 10
- API Security
- Active Directory Security
- Network Pentesting
- Wireless Security
- Cloud Security
- Kubernetes Security
- Mobile Security
- Malware Analysis
- Bug Bounty Hunting
- AI & LLM Security
- Security Consulting
- Security Reporting
- Python for Offensive Security
These skills can help learners build a foundation for different offensive security and ethical hacking career paths.
Career Prospects After Ethical Hacking Training
The cyber security industry offers multiple career paths for professionals with offensive security skills.
Depending on experience, technical abilities, specialization, certifications, and professional development, learners can explore roles such as:
Ethical Hacker
Ethical Hackers assess systems and applications with proper authorization to identify vulnerabilities and security weaknesses.
Penetration Tester
Penetration Testers perform controlled security assessments to identify vulnerabilities in networks, applications, systems, and infrastructure.
Security Consultant
Security Consultants help organizations understand security risks and recommend improvements based on security assessments and business requirements.
Red Team Operator
Red Team Operators simulate adversarial activities in authorized environments to evaluate an organization’s ability to prevent and respond to sophisticated attacks.
Application Security Engineer
Application Security Engineers focus on identifying and reducing security risks in software applications and development processes.
Vulnerability Assessor
Vulnerability Assessors identify, analyze, prioritize, and document security weaknesses across authorized systems and infrastructure.
Bug Bounty Researcher
Bug Bounty Researchers identify vulnerabilities within authorized bug bounty programs and responsibly report them to the relevant organizations.
Expected Salary in Cyber Security
Cyber security salaries vary according to experience, technical skills, specialization, organization, location, job responsibilities, and market conditions.
Indicative salary ranges for offensive security professionals are:
Freshers: ₹5–10 LPA
Mid-Level: ₹10–20 LPA
Experienced: ₹20–30+ LPA
These are indicative ranges rather than guaranteed salaries. Actual compensation can vary significantly based on individual skills, experience, employer, role, certifications, and industry.
Who Can Join This Ethical Hacking Course?
The Master Offensive Security & Red Team Program is designed for learners from a variety of educational and professional backgrounds.
Eligibility
- 12th Pass Students
- Graduates
- BCA Students
- MCA Students
- B.Tech Students
- Diploma Students
- IT Students
- Working Professionals
- Aspiring Ethical Hackers
- IT Professionals looking to upgrade their security skills
A basic understanding of computers and networking can be beneficial. Learners with an IT, programming, networking, or system administration background may find it easier to understand advanced technical concepts.
Why Choose SRC for Advanced Cyber Security Training?
Cyber security is a highly technical field, so selecting a structured training program is important.
The SRC Master Offensive Security & Red Team Program is designed around a broad range of modern offensive security topics.
Comprehensive Curriculum
The program covers networking, operating systems, Python, reconnaissance, OSINT, web security, API security, Active Directory, network penetration testing, cloud security, Kubernetes, mobile security, Red Team operations, Bug Bounty Hunting, and AI & LLM Security.
Career-Oriented Learning
The curriculum is aligned with different offensive security career paths, including ethical hacking, penetration testing, vulnerability assessment, application security, Red Team operations, and security consulting.
Modern Security Topics
The program includes emerging areas such as Kubernetes Security and AI & LLM Security, helping learners understand how the cyber security landscape is evolving.
Structured Learning Path
Students can progress from foundational concepts toward more advanced offensive security topics in a structured manner.
Suitable for Students & Professionals
The program is suitable for students, graduates, IT professionals, and working professionals who want to develop or upgrade their cyber security skills.
Ethical Hacking vs. Malicious Hacking
Ethical hacking and malicious hacking are fundamentally different.
Ethical hackers work with authorization to identify vulnerabilities and help organizations improve their security.
Malicious attackers attempt to access systems without authorization and may steal information, disrupt services, or cause financial and operational damage.
The Master Offensive Security & Red Team Program focuses on responsible and authorized security testing. Learners should always perform security assessments only within approved environments and defined scopes.
Build Your Career in Offensive Security
Cyber security is continuously evolving, and organizations need professionals who can understand security from an attacker’s perspective while operating within legal and ethical boundaries.
Learning offensive security can open pathways into ethical hacking, penetration testing, vulnerability assessment, application security, Red Team operations, security consulting, and bug bounty research.
The Advanced Cyber Security & Ethical Hacking – Master Offensive Security & Red Team Program at SRC provides a structured learning journey covering the essential foundations and advanced areas of modern offensive security.
From Networking and Linux to Reconnaissance, OSINT, Web Security, API Security, Active Directory, Network Pentesting, Cloud Security, Kubernetes Security, Mobile Security, Red Team Operations, Bug Bounty Hunting, and AI & LLM Security, the program is designed to give learners broad exposure to today’s cyber security landscape.
Start Your Offensive Security Journey
Develop technical knowledge.
Understand security vulnerabilities.
Learn offensive security methodologies.
Build skills for modern cyber security roles.
Join SRC’s Master Offensive Security & Red Team Program and take your next step toward a professional career in Cyber Security.
Frequently Asked Questions
1. What is the Master Offensive Security & Red Team Program?
It is an advanced cyber security training program focused on ethical hacking, penetration testing, Red Team operations, vulnerability assessment, application security, cloud security, Bug Bounty Hunting, and modern offensive security.
2. Who can join the Ethical Hacking course?
12th pass students, graduates, BCA, MCA, B.Tech, diploma students, IT learners, and working professionals can join the program.
3. Is this course suitable for beginners?
The program starts with foundational topics such as networking and operating systems before moving toward advanced offensive security concepts. A basic understanding of computers can be helpful.
4. What career opportunities are available after Ethical Hacking training?
Depending on skills and experience, learners can explore roles such as Ethical Hacker, Penetration Tester, Security Consultant, Red Team Operator, Application Security Engineer, Vulnerability Assessor, and Bug Bounty Researcher.
5. Does the course cover Web Application Security?
Yes. The program covers Web Fundamentals, OWASP Top 10, Advanced Web Security, and API Security Testing.
6. Does the course cover Red Team Operations?
Yes. Red Team Foundations is included in the program, providing an introduction to authorized adversary simulation and offensive security operations.
7. Does the program include Bug Bounty Hunting?
Yes. The curriculum includes Bug Bounty Hunting concepts, vulnerability research, responsible disclosure, and security reporting.
8. Does the course cover Cloud Security?
Yes. Cloud Security and Kubernetes Security are included in the program.
9. Does the program cover AI and LLM Security?
Yes. AI & LLM Security is included to introduce learners to emerging security considerations associated with AI-powered applications and large language models.
10. What salary can an Ethical Hacker expect?
Salary depends on experience, skills, specialization, company, location, and job role. Indicative ranges are ₹5–10 LPA for freshers, ₹10–20 LPA for mid-level professionals, and ₹20–30+ LPA for experienced professionals.
11. Is Python included in the program?
Yes. The program includes Python for Offensive Security, helping learners understand how scripting and automation can support authorized security assessment activities.
12. Why learn Offensive Security?
Offensive Security helps organizations proactively identify vulnerabilities before they can be exploited by malicious attackers. Developing these skills can help learners prepare for multiple cyber security career paths.
Take the Next Step Toward a Cyber Security Career
The future of cyber security requires professionals